
 Özgül Yavuz Kaddoura
Updated Date:
Botnet Click Fraud: How to Detect and Stop Attacks
How Botnet Click Fraud Drains Your Ad Budget
Your Google Ads campaign looks healthy at first glance: impressions are up and your click-through rate (CTR) is climbing. Yet your budget runs out faster than usual, and sales or leads aren't growing. One possible reason is a botnet, a network of infected computers and phones that clicks your ads automatically. In this guide, we explain how botnet click fraud works, how to spot it in your account and how to stop it.
What Is the Difference Between a Bot and a Botnet?
A bot is a software program that performs tasks automatically. In ad fraud, bots are built to imitate real users: they visit websites and click on ads. On its own, a single bot is relatively easy to stop, because its clicks come from one device or IP address.
A botnet, short for "robot network," is much harder to stop. It's a network of thousands or even millions of computers, phones and other connected devices that have been infected with malware, usually without their owners knowing. A single operator controls them all and can direct them to click your ads in a coordinated way, often spreading the clicks across many devices and hours so they look like normal traffic. For real-world examples, see our guide to click fraud bots and botnets like Methbot and 3ve.
Why Fraudsters Use Botnets for Click Fraud
Fraudsters use botnets for click fraud because they offer three advantages over single bots:
| Scale | One operator can generate large numbers of clicks across many devices, enough to use up a daily budget long before you notice. |
| Disguise | Each click comes from a different device and IP address, often on ordinary home and mobile connections, so the attack can look like a genuine rise in interest and slip past basic filters. |
| Low cost, high payoff | Fraudsters either run their own low-quality websites and apps that show Display ads and earn money from every fake click, or are hired by unethical competitors to drain a rival's budget. Running a botnet costs far less than the ad spend it wastes. |

How to Spot a Botnet Attack
Botnet attacks blend in, but they leave patterns. Watch for these warning signs:
| Clicks up, sales flat | More clicks, but no rise in sales or leads. |
| Many IPs, no engagement | Clicks from many IPs, each once or twice, with no conversions. |
| Odd locations | Traffic from regions outside your target market. |
| Weak placements | Display, Performance Max or YouTube placements with clicks but no conversions. |
| Unnatural behavior | Visits ending in seconds, unusually high CTRs or off-hours activity. |
One sign alone isn't proof; several together usually are.
How ClickSambo Stops Botnet Click Fraud
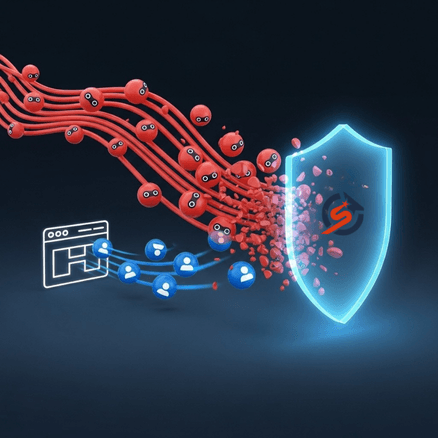
Botnet clicks come from many home and mobile devices, so blocking IPs one by one isn't enough. ClickSambo combines several layers on your Google Ads and Meta Ads campaigns:
| Behavioral AI | Separates automated traffic from real users by how they interact with your site. |
| Device fingerprinting | Stable Device ID recognizes the same device even when its IP changes. |
| VPN, proxy and Tor detection | Flags traffic that hides its real origin. |
| Customizable rules | Click velocity thresholds block devices or IPs that click too often. |
Suspicious sources are excluded on Google Ads, and on Meta Ads, suspicious traffic is blocked from reaching your campaigns.

Botnets hide behind ordinary home IPs. ClickSambo recognizes devices, not just IP addresses, and blocks suspicious sources on your Google Ads and Meta Ads campaigns.
 Start Free Trial
Frequently asked questions
Basic filters are good at catching general invalid traffic (GIVT), such as known data center IPs, known bots and repeated clicks from one source. Google catches much more than that, but some botnet traffic still gets through, because botnets use large numbers of infected home computers and phones. Each click comes from a different device with an ordinary home or mobile IP address, so it can pass simple frequency limits and IP-based checks. Catching it requires looking at the device and behavior behind each click, not just the IP address.
Command and control (C&C) is the system a botnet operator uses to send instructions to infected devices, often called "zombies." Through it, the operator can tell thousands of devices which ads to click, when and how often. Rather than clicking all at once, which would be easy to spot, botnets usually spread their clicks across many devices and hours so they look like normal traffic. This is why botnet attacks can quietly drain a budget before anyone notices, and why checking every click automatically works better than reviewing reports by hand.
It's possible, but less common than you might think. Some infected smart devices, such as smart TVs and streaming boxes, have been used in ad fraud, especially for video and connected TV ads. Many IoT botnets, however, are mainly used for other attacks, like overwhelming websites with traffic. Most botnet click fraud on search and display ads still comes from infected computers and smartphones, which can run full browsers and look like ordinary home visitors.
ClickSambo looks beyond the IP address. Its Stable Device ID recognizes the same device across many clicks, even when a botnet switches to a new home or mobile IP. Behavioral AI analyzes how each visitor interacts with your site to separate automated traffic from real users, while VPN and proxy detection and click velocity thresholds catch the patterns botnets use to hide. Suspicious sources are blocked automatically, so they can't keep clicking your Google Ads and Meta Ads campaigns.


 Other